AI Generated Writeups Imported from Chat History
Project / / 1 min read
Hardware-backed Linux authentication
Integrating a YubiKey with Linux authentication, SSH, sudo, and the Hyprlock session lock screen.
Overview
I integrated a YubiKey 5C into my Linux authentication workflow. The setup uses FIDO2 and U2F credentials with OpenSSH, PAM, sudo, and Hyprlock.
The goal was to use hardware-backed authentication for everyday access while keeping the system usable when the key is unavailable.
SSH and system authentication
I created resident FIDO-backed SSH keys and worked with downloading resident credentials. The configuration includes PIN and user-presence verification for the key, along with PAM U2F authentication for sudo.
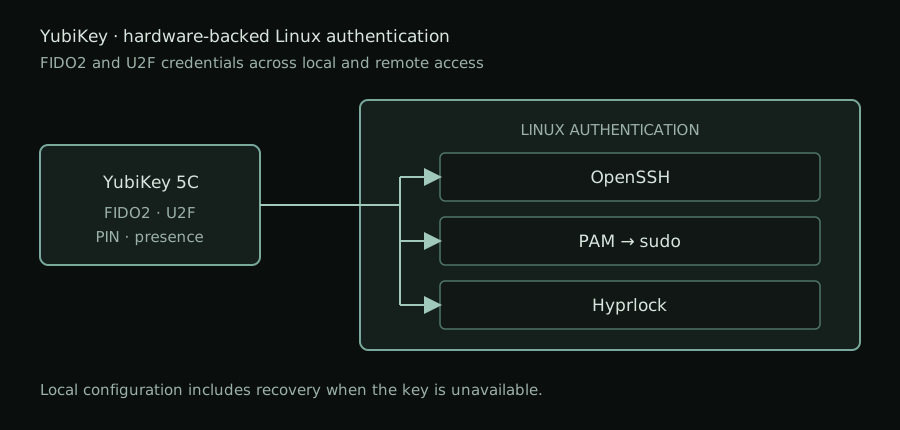
The workflow also includes Linux device events and lock behavior when the key is removed. I tested how graphical lock-screen prompts behave and how authentication should fall back when the hardware key is not present.
Result
The YubiKey is integrated into SSH access, privileged commands through sudo, and the Hyprlock session lock screen. The project combines FIDO2 credentials, PAM configuration, desktop-session behavior, and recovery considerations in one Linux authentication workflow.